Exterro brings Information Governance leaders a unified way to find, analyze, and protect enterprise data by aligning retention policy creation and enforcement on one platform.
.jpg)
Information governance professionals struggle to maintain a clear understanding of the data their organizations hold and the legal and regulatory obligations tied to it across complex on-premises, cloud, and hybrid environments. Managing these environments with disconnected tools increases change management, retraining, and inefficiencies across teams.
Exterro meets the compliance and data management needs of information governance professionals in a purpose-built, unified platform powered by deep data insight.
.jpg)
From data mapping and defensible deletion to supporting legal and privacy teams around litigation and compliance, explore the use cases that Exterro can help you work smarter.
.jpg)

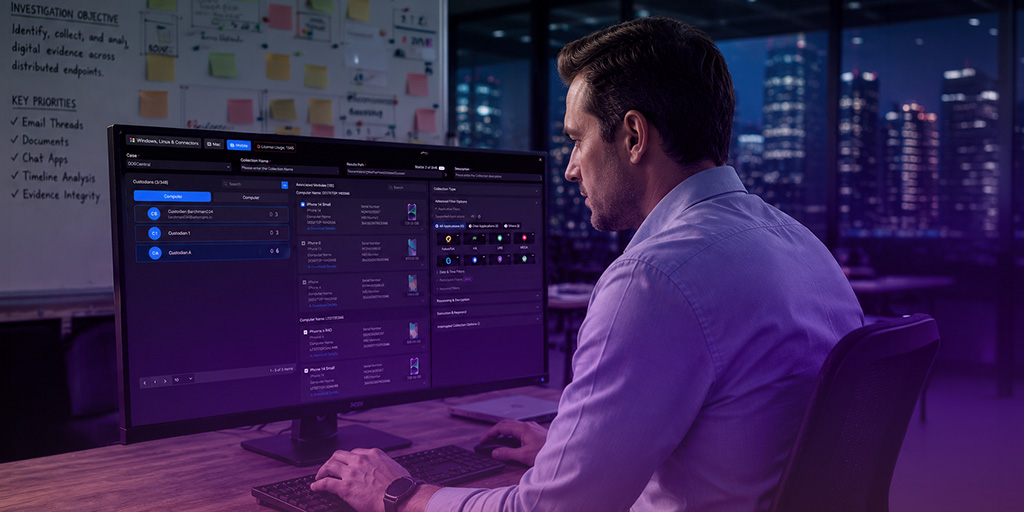
Built into the Exterro Platform, Exterro Intelligence helps you uncover your data, prioritize what matters, preserve defensibly, execute efficiently, and document every step with complete auditability.

Scan structured and unstructured repositories across cloud and on-premise infrastructure using automated data discovery connectors.

Apply continuous AI-driven classification rules to categorize records by data type, jurisdiction, and applicable retention schedules.

Automatically cross-reference target files against active litigation holds in Exterro Legal Hold to prevent accidental destruction of relevant evidence.

Route deletion requests to data owners, privacy officers, and legal teams through automated notification workflows.

Permanently purge expired data across connected systems and generate an immutable, regulator-ready certificate of disposition.
Everything you need to know about how Exterro helps support key elements of the information governance lifecycle.
Information Governance (IG) is an enterprise strategy and policy framework that manages data assets throughout their lifecycle to balance business utility against legal, regulatory, and security risks. Rather than managing data in silos, IG unifies privacy, legal, and IT operations under a single policy engine. This unified structure ensures organizations satisfy the data stewardship mandates of GDPR (EU), CPRA (California), and HIPAA (healthcare) by maintaining continuous control, visibility, and accountability over sensitive records.
Defensible disposition is the systematic, auditable, and legal destruction of enterprise data once it reaches the end of its required operational, legal, or regulatory retention lifecycle. Under GDPR Article 5(1)(e)—the "storage limitation" principle—personal data must not be kept longer than necessary for its original processing purpose. Defensible disposition enforces this rule by automatically identifying expired personal data and executing permanent deletion alongside an immutable audit trail to prove compliance to supervisory authorities.
Data minimization is the practice of restricting the collection, processing, and storage of personal information to only what is strictly necessary to fulfill a specific, disclosed purpose. Enforced by GDPR Article 5(1)(c) and CPRA § 1798.100, data minimization prevents "data hoarding." Information Governance operationalizes this principle by using automated scanning policies to flag excessive data collection, eliminate redundant files at intake, and prevent unneeded personal data from entering downstream environments.
ROT data refers to Redundant, Obsolete, and Trivial information that holds zero operational, financial, or legal value to an organization. Under Federal Rule of Civil Procedure (FRCP) 26, retaining ROT dramatically inflates the scope, cost, and time required to execute legal discovery during litigation. An IG program systematically purges ROT, reducing the total volume of discoverable data, lowering eDiscovery vendor processing costs, and cutting breach exposure under privacy statutes like the CCPA.
A data inventory (or data map) is a dynamic, structured index of an organization’s data assets, detailing where data resides, who owns it, how it flows, and what security controls protect it. A comprehensive data inventory serves as the technical baseline for generating a Record of Processing Activities (RoPA) as required by GDPR Article 30. It also enables organizations to fulfill CPRA obligations that mandate informing consumers at or before the point of collection about the exact categories of data being collected and their corresponding retention periods.
Dark data is unmanaged, unclassified operational information that an organization collects, processes, and stores during regular business activities but fails to track or audit. Dark data frequently contains exposed sensitive PII, intellectual property, or financial records. Governing dark data via automated IG discovery tools ensures these hidden assets are classified, secured, or deleted—mitigating severe penalties under emerging frameworks like the EU NIS2 Directive and SEC Cybersecurity Disclosure rules that penalize unmanaged vulnerabilities and undisclosed breaches.
Data Lifecycle Management (DLM) is a policy-driven approach to overseeing enterprise data from creation and initial ingestion through storage, maintenance, and ultimate disposition. Under the EU AI Act (Article 10), organizations deploying high-risk artificial intelligence models are legally required to enforce strict data governance standards over training, validation, and testing datasets. DLM provides the necessary structure to ensure AI training data is accurate, representative, free of unapproved personal data, and fully traceable across its lifecycle.
FRCP Rule 37(e) authorizes federal courts to penalize organizations if electronically stored information (ESI) that should have been preserved in the anticipation of litigation is lost because a party failed to take reasonable steps to preserve it. An Information Governance framework connects retention engines directly to legal hold automation. When a legal hold is issued, the IG system automatically pauses routine automated deletion policies for relevant data subjects or repositories, protecting the organization from spoliation sanctions while allowing defensible disposition to continue for unaffected data.
See our data governance solutions in action.