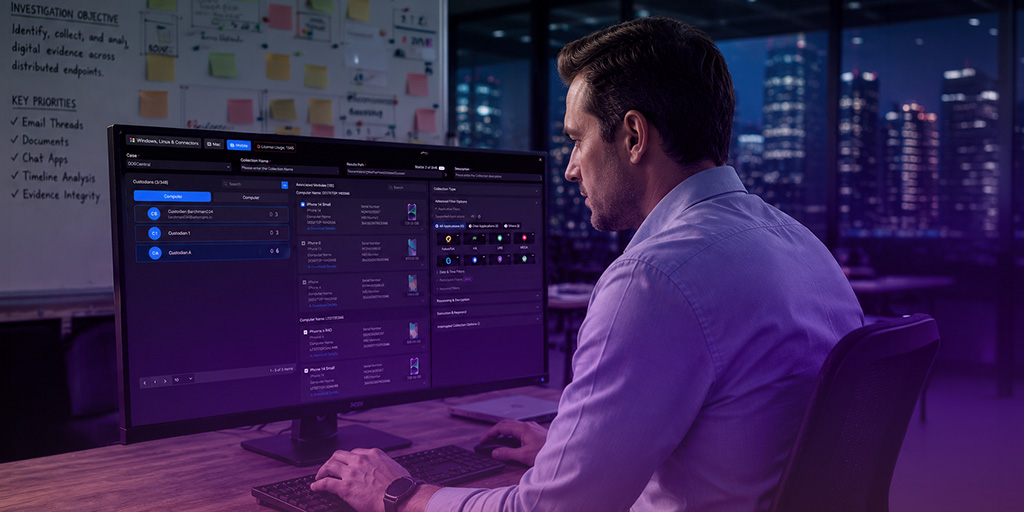
Your eDiscovery Platform Is Built. Your Coordination Layer Isn't.
Where Should Governed AI Sit Inside an Established eDiscovery Workflow?
Authored by Bryant Bell, Sr. Product Marketing Manager, eDiscovery & AI, Exterro
TL;DR
- Established eDiscovery platforms handle discrete tasks well, but consequential decisions about hold scope, privilege designations, and escalation timing move outside the platform into email threads and institutional knowledge, creating defensibility risk that doesn't appear on any dashboard.
- Legal teams leave audit trails incomplete and cannot consistently demonstrate multi-jurisdiction compliance across the coordination gap between capable systems.
- Legal teams close that gap when they operate governed AI through existing workflows, permissions, and playbooks rather than beside them, with every automated action logged, attributed, and audit-ready.
- One measured customer result reduced a review set of 138,000 documents to 3,300, a 97 percent reduction, by identifying relevant material earlier in the process.
- The decision general counsels face is whether the governed AI their legal teams adopt will work inside the governance structure they have already built.
Legal teams that built their eDiscovery infrastructure over years made the right call. The platforms handle collection, review, hold management, and production. The workflows are established. The governance foundation is real.
Except that matter volume keeps climbing, regulatory timelines keep compressing, and the coordination holding those capable systems together still relies on manual effort. Technology vendors built capable point solutions but left the coordination gap open.
Coordinators still route matter status through email threads, personal knowledge, and manual handoffs that leave consequential decisions unlogged and audit trails incomplete. Whether governed AI works inside the governance structure legal teams have already built determines whether existing platform investments scale or stall under their own coordination costs.
The Oversight Gaps Inside Established Legal Technology
While established platforms handle document collection, review queues, hold notices, and production workflows effectively, problems surface in the space between those jobs.
Decisions about hold scope, privilege designations, cross-matter data treatment, and escalation timing move outside the platform. They land in email threads, phone conversations, and the institutional knowledge of two or three senior coordinators. The work gets done. The record of how it got done doesn't.
Litigators call that gap a defensibility problem.
When manual coordination becomes the connective tissue between capable but disconnected systems, several compounding risks develop:
- Teams accumulate accountability gaps silently. Approval decisions that travel by email or verbal instruction don't generate the timestamped, role-attributed records that litigation and regulatory scrutiny require. Reconstructing who authorized what becomes a research project rather than a report.
- Legal teams cannot consistently demonstrate multi-jurisdiction compliance. Fragmented data access means privacy controls and privilege designations may be enforced in one jurisdiction and invisible in another.
- Legal departments face concentrated operational risk when they depend on power users. When matter context and prior legal decisions live in a few people's heads, departures and capacity crunches become threats to matter continuity, not just inconveniences.
None of these risks appear on a dashboard. General counsels who can't track approvals across teams aren't failing at governance. Their tools aren't giving governance a place to live.
The issue isn't platform selection. Established platforms handle discrete tasks while manual coordination handles everything in between. Those two things together don't equal a controlled process. They equal a partially controlled process with unmonitored gaps.
Governed AI Benefits in Existing eDiscovery Workflows
General counsels are no longer asking whether to use AI in legal operations. They are asking where AI earns its place and under what conditions legal teams can trust what it does.
Governed AI belongs inside the eDiscovery process, working through the systems, permissions, and playbooks legal teams already maintain—not beside them, not layered on top. Through them.
Exterro ARMOUR (Autonomous Risk Management, Orchestration, and Unified Response) makes this practical through four operating principles:
- Orchestrated, auditable action across existing workflows: Exterro ARMOUR translates legal instructions into coordinated actions across eDiscovery workflows, with every step attributed, logged, and audit-ready. Legal teams don't need to change how they think about a matter. The platform translates that thinking into traceable workflow execution.
- Persistent matter context that carries forward: Exterro Intelligence lets legal teams carry trusted legal intelligence forward, applying what was validated in prior matters rather than recreating it from scratch, eliminating the work of rebuilding custodian scope and privilege positions for every new matter.
- Earlier identification of what actually matters: A measured customer result illustrates this at scale: a review set of 138,000 documents was reduced to 3,300—a 97 percent reduction—by identifying what was relevant earlier in the process. AI-assisted early case assessment helps legal teams prioritize review, support defensible legal spend reduction, and protect human judgment for decisions that carry real risk.
- Unified data governance across jurisdictions: Legal teams use single-instance storage to reduce duplicate data handling and apply consistent legal designations across matters, teams, and regions, without custom configurations for each jurisdiction.
Angie Nolet, Corporate Counsel, says "Exterro has made our job easier a hundred-fold. We are so much more organized. The control that we can exercise over our data gives us a lot more confidence in its security and in our litigation costs. We're working smarter, not harder."
Governed AI, applied this way, doesn't ask legal teams to trust the model. It asks them to define the rules, set the approval gates, and let controlled automation execute within those boundaries. Legal judgment stays where it belongs: on the decisions that require it.
Deliberate Change from Manual Coordination to Coordinated Workflows
For legal teams managing larger matter volumes, expanding data sources, and stricter regulatory expectations, the shift from coordination by exception to coordination by design is where capacity actually changes.
Consider what this looks like across four repeatable areas of eDiscovery operations:
- Legal hold and custodian management: Automated legal hold and custodian management help legal teams issue holds, track acknowledgments, escalate non-responses, and document every action—timestamped, attributed, and living in the platform.
- Request and subpoena workflows: Request and subpoena workflow automation structures intake, assigns ownership, monitors status, and reports progress with fewer manual checkpoints. Legal teams handle higher volumes without proportionally increasing manual oversight because the workflow itself maintains the record.
- Governed playbooks across matters and regions: Legal operations leaders encode approved processes into governed playbooks so legal teams apply consistent steps across matters, regions, and business units. When a new matter lands, the playbook defines the steps, the approvers, and the documentation requirements before the first coordinator touches the file.
- Connected matter intelligence: Exterro ARMOUR connects matter history, workflow status, permissions, and prior legal decisions to accelerate matter execution, so context accumulates, decisions are retrievable, and prior work informs current matters rather than sitting inert in closed files.
This is an operational model change, not a technology upgrade. Legal teams move from managing coordination manually to managing the workflow itself, with AI executing within defined boundaries and humans retaining authority over consequential decisions. The result: more matters handled with existing resources, reduced outside counsel dependence, and audit trails generated automatically rather than reconstructed after the fact.
Expansion of eDiscovery Benefits and Maintenance of Defensibility
General counsels who have built strong eDiscovery foundations now face a straightforward decision about where their next operational capacity comes from. Headcount scales linearly. Workflow intelligence doesn't.
Legal teams that embed privacy-first governance and audit-ready reporting at the workflow level, rather than applying them case by case, will find that compliance and capacity move together rather than against each other.
Explore more: Read Exterro's guide to defensible legal workflow automation and eDiscovery governance to see how legal teams apply governed AI across matter management, legal hold, and document review.
Stay current: Subscribe for practical insights on Trusted AI, data risk management, and legal operations maturity—delivered for practitioners managing real operational decisions.
Frequently Asked Questions
How Can Governed AI Improve eDiscovery Without Reducing Legal Oversight?
Governed AI improves eDiscovery when legal teams define playbooks, approval gates, role-based permissions, and audit requirements before controlled automation executes routine work. ARMOUR for eDiscovery encodes those definitions into the workflow, so every automated action operates within boundaries that legal teams set and control. Human judgment remains in place for consequential decisions, and every step is logged, attributed, and audit-ready.
Why Do Auditability Gaps Still Exist in Established eDiscovery Systems?
Established systems leave gaps when decisions, approvals, and status updates move outside the platform through email, spreadsheets, and informal handoffs. The platforms themselves may be capable. The coordination between them often isn't controlled or documented. That uncontrolled space is where defensibility risk accumulates.
What Makes Exterro ARMOUR Different From Adding Another Legal Technology Tool?
Exterro ARMOUR focuses on orchestrated workflows, persistent matter context, single-instance storage, and governed automation that activates more value from the systems and data legal teams already use. It doesn't add a parallel environment to manage. It makes the existing Exterro environment more coordinated, more auditable, and more capable of scaling with matter demand.