Identity as the Perimeter: How Avant Tackles Data Proliferation, Privacy, and AI Risk
As financial services scale their operations in cloud-native environments, the volume, complexity, and velocity of consumer data are testing the limits of traditional security and governance playbooks. On a recent episode of the Data Xposure podcast, host Fahad Diwan sat down with Rudy Ristich, Chief Information Security Officer and Chief Privacy Officer at fintech lender Avant, to explore how modern risk leaders are managing this shift.
From dismantling the wall between security and privacy to automating data classification and managing non-human machine identities, Ristich outlined a pragmatic blueprint for protecting enterprise data while accelerating innovation.
Listen to the podcast episode Most of the Things Accessing Your Data Aren’t People Anymore here.
Merging the Remit: Protecting the Box vs. Governing the Contents
While information security and privacy have historically functioned in separate corporate silos, leaders are increasingly uniting both remits under a single mandate.
The distinction boils down to a simple operational analogy:
- Information Security: Protecting the box that holds the data.
- Privacy: Ensuring that data inside the box is handled ethically, legally, and in compliance with regulatory standards.
At Avant—a company dedicated to expanding access to credit for the middle class—data controls form the connective tissue between both responsibilities. By consolidating security and privacy governance, organizations can ensure that data protection controls and regulatory compliance obligations scale together across the entire customer lifecycle.
"Data Record Beats Data Recollection": The Move to Automated Classification
For growing enterprises, keeping track of where sensitive data flows after leaving core structured databases is a persistent headache. Many organizations still rely on legacy methods like manual department surveys and stakeholder interviews, which carry significant structural flaws:
- Subjective Definitions: Even when given strict compliance criteria, internal teams interpret terms like "personally identifiable information" (PII) inconsistently.
- Static Point-in-Time Snapshots: A manual interview captures an employee's recollection at a single moment, rendering the inventory obsolete months before the next review.
- Scale Mismatches: When third-party systems and data repositories outnumber internal employees, human-driven tracking becomes mathematically impossible to sustain.
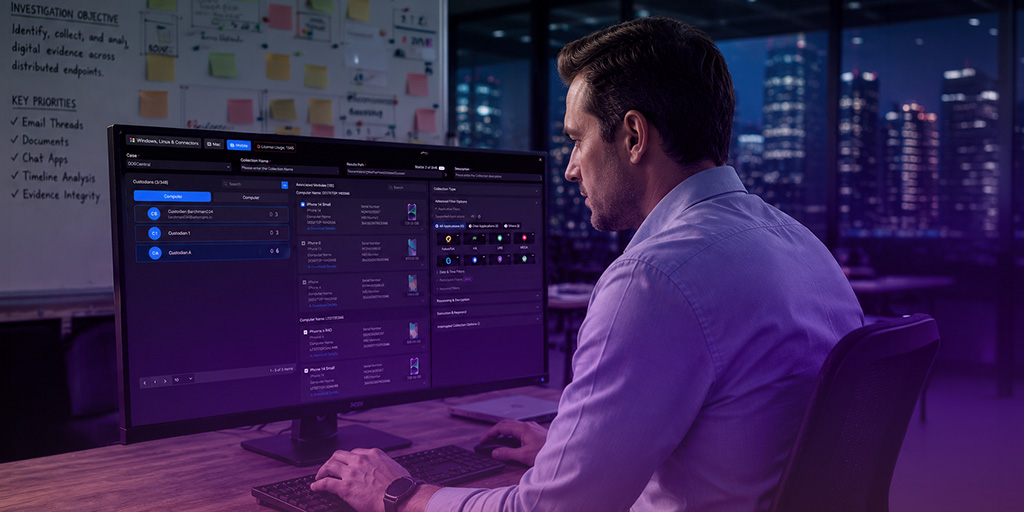
To solve this, Avant is deploying automated platforms like Exterro OptiX360 to scan and classify structured and unstructured data at scale. By shifting from manual recollection to continuous, technical scanning, security teams achieve an evergreen data inventory. Machine-assisted labeling allows data protection specialists to validate classifications accurately, creating the foundation for automated data hygiene and lifecycle retention programs.
Balancing Innovation with Guardrails in the Age of AI
Enterprises cannot afford to ignore emerging frontier AI capabilities, but moving fast without clear controls introduces substantial operational and legal vulnerabilities.
To stay agile without breaking compliance, Avant relies on a structured cross-functional governance rhythm:
- Bi-Weekly Alignment: Security and privacy leaders meet bi-weekly with legal counsel, compliance teams, and the CIO’s designated "AI champions".
- Business Enablement with Guardrails: Rather than acting as a roadblock, security teams evaluate the business objective first, establishing contractual, technical, and regulatory guardrails so teams can adopt tools safely.
- Ad-Hoc Risk Reviews: For rapid releases from frontier AI labs, teams conduct immediate, holistic risk assessments to decide when to accelerate adoption and when to pump the brakes.
Fighting Fire with Fire: Novel AI Threats and Defensive Countermeasures
The democratization of AI has lowered the barrier to entry for threat actors, introducing novel risks to consumer lending and financial platforms:
- Hyper-Targeted Pretexting: Attackers use generative tools to conduct deep reconnaissance, crafting sophisticated phishing and Business Email Compromise (BEC) campaigns that easily bypass standard employee skepticism.
- Identity Fraud & Deepfakes: Sophisticated synthetic identities, document spoofing, and deepfakes demand continuously evolving identity verification countermeasures.
Defenders, however, are leveraging the same technologies to build asymmetric advantages. Internally, security teams are deploying AI to accelerate complex infrastructure scanning, proactively detect unused platform capabilities, and streamline vendor risk management. For example, when third-party vendors submit machine-generated security questionnaires, internal teams use AI models to analyze, consolidate, and review audit reports in a fraction of the time required by manual human review.
Three Core Mandates for Modern Enterprise Data Security
Closing out the discussion, Ristich highlighted three fundamental priorities every enterprise leader must implement to secure their data footprint:
- Know Exactly What You Have: You cannot protect or govern what you cannot see. Prioritize real-time, automated discovery over manual point-in-time assessments to maintain continuous visibility across cloud and vendor environments.
- Enforce Fundamental Controls: Layer foundational defenses directly around sensitive data assets. Mandate multi-factor authentication (MFA), adopt zero-trust architectures, and ensure no single set of credentials grants unrestricted access to consumer records.
- Treat Identity as the Perimeter (Humans and Agents Alike): In cloud-native ecosystems, network perimeters have largely dissolved in favor of identity. Security teams must strictly govern not only human accounts, but also the expanding roster of automated agents, bots, and machine identities executing workflows across the environment.
As AI agents take on operational workloads alongside human staff, securing digital workers becomes just as critical as managing traditional credentials. Organizations that combine continuous data discovery with robust identity governance will be best positioned to innovate rapidly without sacrificing consumer trust.
Listen to the full conversation between Rudy Ristich and Fahad Diwan here.