Finding the Answer Inside a Large Collection: Internal Investigations with FTK 8.3
Authored by Robert Bond, Senior Product Marketing Manager, Digital Forensics, Exterro
Most internal investigations begin the same way. Something has been reported: a policy violation, an allegation of unauthorized data access, a concern raised about someone's conduct. The matter is sensitive, the population of potentially relevant data is large, and nobody yet knows which part of it holds the answer.
What follows is rarely a technical problem. It is a search problem, a scale problem, and a time problem - usually all three at once.
Where the time actually goes
Collection is scattered before it is even started. Evidence sits across distributed and remote environments, on Windows, Mac, Linux, mobile and other endpoint sources. Teams need collection workflows that are consistent, visible and defensible across real-world systems and when they are not, the first days of an investigation are spent assembling the data rather than examining it.
Processing queues up behind the collection. Endpoint collections, mobile data, structured application records, communications and system activity all have to be processed, organized and prepared before anyone can begin meaningful analysis. Every hour lost before review begins increases downstream pressure on examiners, reviewers, legal teams, security teams, and anyone waiting on the outcome.
Then the real problem starts. Investigators lose time searching and filtering to find relevant facts within a large collection. Emails, chats, file activity, browser activity, mobile data, application records and endpoint evidence all have to be worked through and early in a case there is no reliable signal about which of them will matter. The investigation proceeds by informed guessing.
And some of the evidence is not in the places anyone is looking. Application and structured data often sits outside the main review workflow. The part of the story recorded inside databases and related artifacts is frequently the part most likely to be missed.
What FTK 8.3 changes
Collection that holds together across platforms
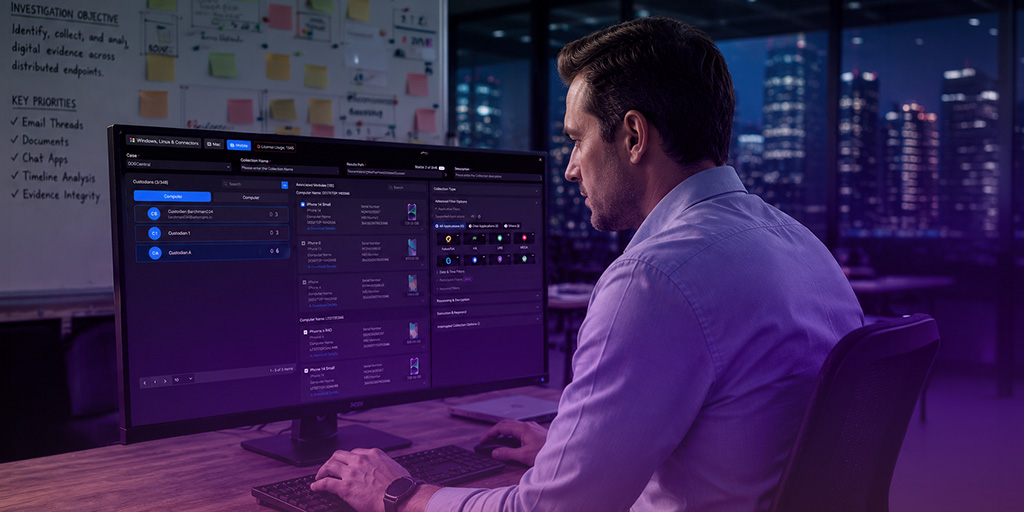
FTK 8.3 includes Endpoint and Collection Enhancements that support investigations across distributed endpoint environments, helping teams improve visibility and control during collection and analysis. The release brings endpoint unification across Windows, macOS, Linux and iOS in a single workflow, with centralized custodian and endpoint visibility, and collected data made automatically available for review.
For an internal investigation, this matters at the outset. A single custodian may have a laptop, a phone and activity on a shared system, and the investigation needs all of it gathered consistently not assembled from three separate processes that have to be reconciled later.
Download the Exterro FTK 8.3 solution brief here.
Processing that keeps up with the collection
Improved Processing at Scale helps teams prepare larger and more complex evidence sets for review and analysis with greater efficiency, reliability and control. FTK 8.3's processing engine modernization brings fault tolerance and the ability to pause, resume and skip within a processing job, alongside full visibility into processing as it runs.
The practical effect in an internal investigation is that a large collection stops being a wall. Processing can be monitored rather than waited on, interrupted work recovers rather than restarts, and evidence moves into review with fewer delays, so the investigation begins while the matter is still current.
A starting point, not a haystack
This is where the investigation actually turns. FTK Data Assist brings AI-assisted investigation directly into the forensic workflow, letting investigators ask natural-language questions, generate contextual summaries, and identify useful starting points, while keeping human judgment central to the process.
That last clause is the important one. FTK Data Assist is designed to help investigators find where to look. It preserves human oversight by design; the investigator reads the underlying evidence and decides what it means. In a sensitive internal matter, where a finding may affect someone's employment, that boundary is not a technicality. It is the difference between a conclusion you can stand behind and one you cannot.
The evidence inside the applications
Database Browser Enhancements support deeper analysis of application and structured data evidence, helping investigators understand activity contained in databases and related artifacts. For internal investigations, this is often where the specific answer lives - what was opened, what was exported, what was accessed and when - in application records that a document-and-email review would never surface.
Review that stays organized
Dynamic Batch Review helps administrators focus review teams on assigned or relevant evidence, reducing noise and improving reviewer productivity. Streamlined Review Workflows improve filtering, organization, export and case review, so teams can move through evidence more efficiently.
In a matter with several people reviewing - HR, legal, an outside firm - this is what keeps the work coordinated and the record clean.
What this adds up to
An internal investigation is judged on whether the conclusion holds. That depends less on any single capability than on whether the whole path from collection to finding stayed intact.
FTK 8.3 addresses the points across that path where teams most often lose time, lose context, or lose momentum: collection that spans platforms, processing that scales with the evidence, AI assistance that points to a starting point without replacing the investigator, structured data brought into the same picture as everything else, and review workflows that keep a multi-person matter coherent.
Less time sorting data. More time understanding evidence.
See it against your own matters
See how Exterro FTK 8.3 can transform how you handle complex evidence sets. Schedule a demo today.